 CoinScoop
Active crypto address 'copy and paste' malware persists despite disruption
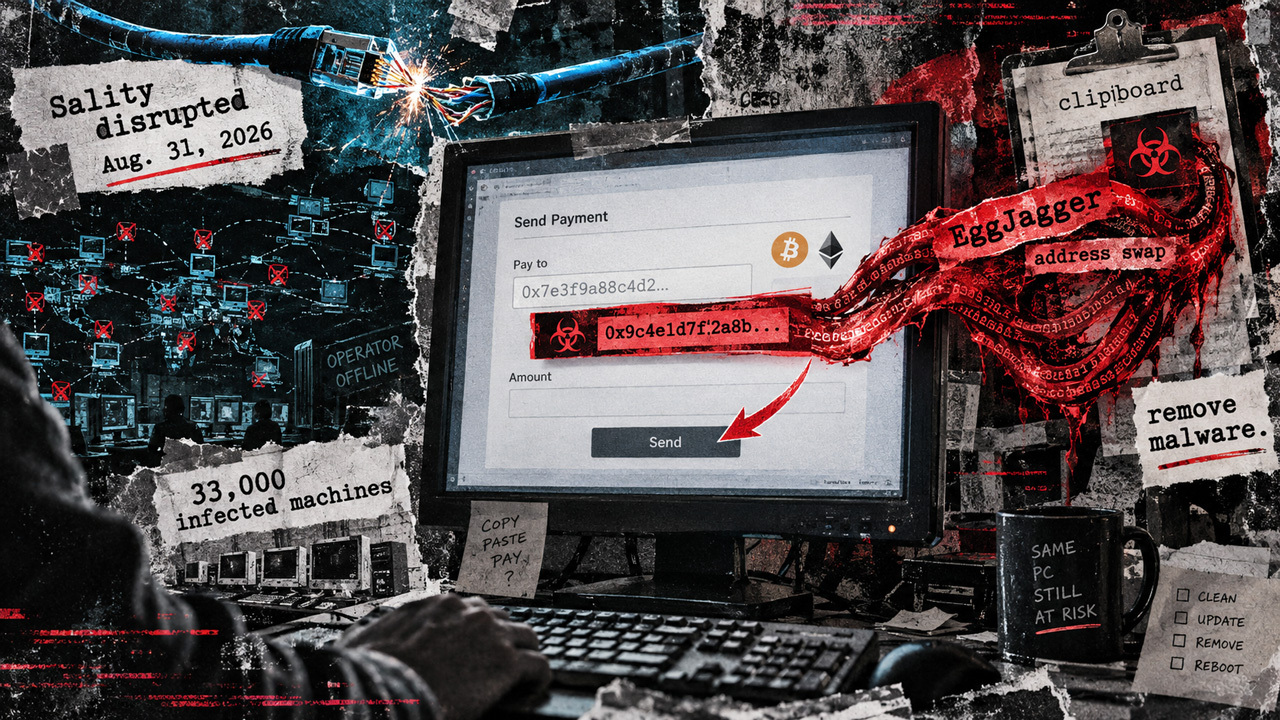
CrowdStrike reported that while the August 31 disruption successfully blocked new payload delivery, previously installed malware remains active. This malware continues to pose a threat by swapping cryptocurrency payment addresses during copy-and-paste operations.
Summaries are written by AI from the original article. Not investment advice.