 CoinScoop
Hacker drains $3 million from GalaChain wallets using failed transaction signatures
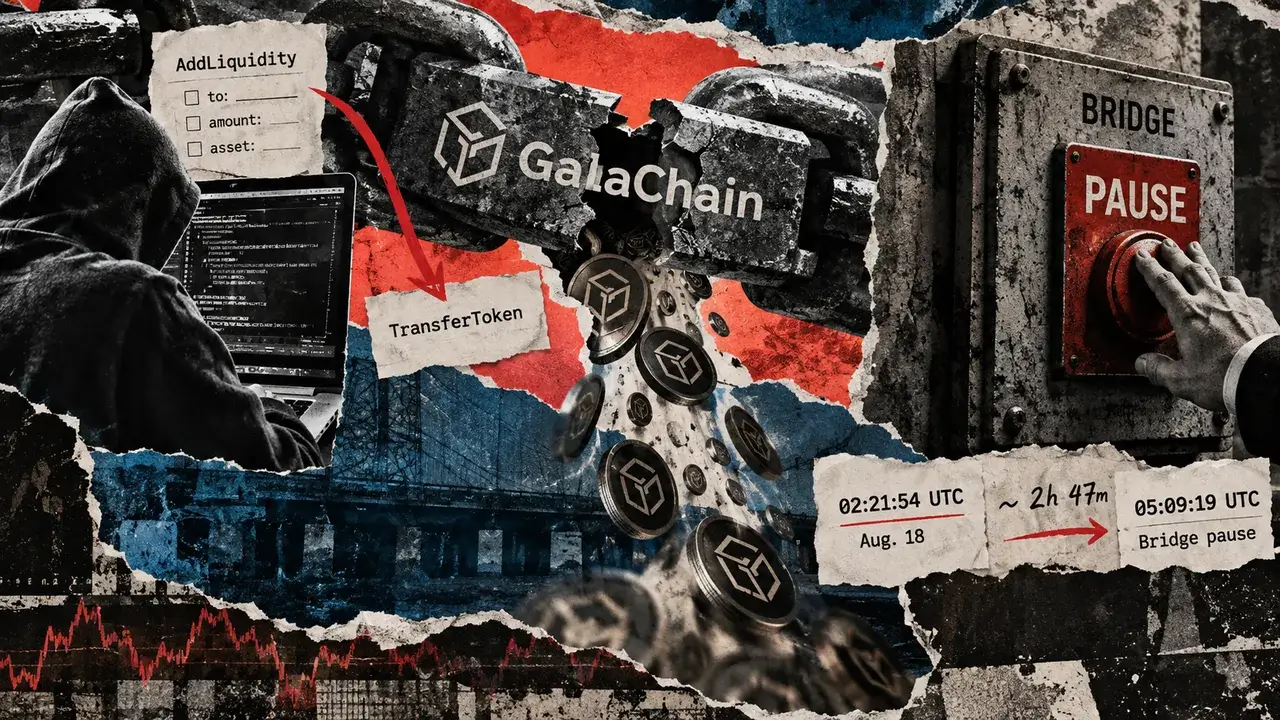
GalaChain suffered an exploit on August 18 where an attacker used 74 reusable signatures from failed transactions to drain approximately 2 billion GALA and other tokens from nine wallets. The vulnerability, which persisted through multiple audits, stemmed from the chain's EIP-712 typed-data verification process, which allowed signatures to be replayed across different operations. The attacker had performed reconnaissance to map account balances before executing the theft with automated submissions.
Summaries are written by AI from the original article. Not investment advice.